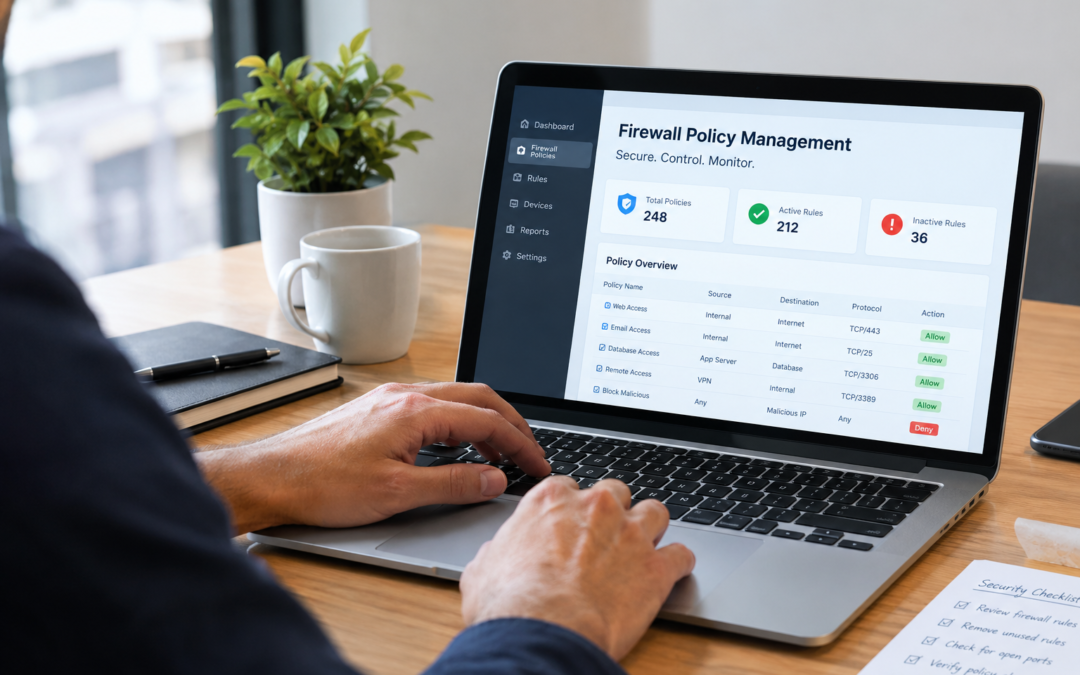
Firewalls remain one of the most important layers of protection for modern networks. They control traffic between systems, applications, users, and external connections, helping organizations prevent unauthorized access and reduce exposure to cyber threats. However, simply having a firewall in place is not enough. As networks grow more complex, the policies and rules controlling that traffic can quickly become difficult to manage.
This is where firewall policy management becomes essential. An effective management approach helps security teams maintain accurate rules, identify unnecessary access, respond to changes, and keep firewall configurations aligned with business and security requirements. Without a structured process, outdated or overly permissive rules can increase risk and make security operations more complicated than they need to be.
Why Firewall Policy Management Matters
Firewall policies determine what network traffic is allowed, blocked, or restricted. Over time, organizations may add new applications, users, locations, cloud environments, and security requirements. Each change can result in additional firewall rules.
The problem is that rules are rarely removed at the same rate they are added.
An organization may eventually have thousands of rules across multiple firewalls. Some may no longer be required, while others may overlap with existing rules or provide broader access than necessary. Security teams may also have difficulty determining why a rule was created, who approved it, or whether it is still being used.
A structured approach makes it easier to maintain these policies and keep them aligned with the organization’s current environment. Instead of treating firewall configuration as a one-time task, teams can manage policies as an ongoing security process.
Establish Clear Policy Ownership
One of the first steps toward better firewall security is establishing clear ownership. Every important rule should have a business or technical reason behind it, along with an understanding of who requested and approved the change.
Without ownership, security teams may hesitate to remove outdated rules because they cannot determine whether an application or business process still depends on them.
Organizations should establish procedures for requesting, reviewing, approving, and documenting firewall changes. This creates accountability and makes future reviews much easier.
Clear ownership is particularly important in large environments where several security and infrastructure teams may be responsible for different firewalls or network segments.
Regularly Review Firewall Rules
Firewall rules should not be considered permanent. Network environments change constantly, and a rule that was necessary several years ago may no longer serve a useful purpose.
Regular reviews can help identify:
- Unused rules
- Duplicate rules
- Overly broad access
- Conflicting rules
- Expired access
- Rules that no longer match business requirements
- Unexpected traffic paths
These reviews can also help security teams prioritize remediation. Not every rule requires immediate attention, so organizations can focus first on configurations that present the greatest security or operational risk.
This process is an important part of effective firewall rule management, especially for organizations operating large or distributed network environments.
Apply the Principle of Least Privilege
A strong firewall strategy should provide only the access that is actually required. Broad permissions can make network administration easier in the short term, but they can also create unnecessary security exposure.
For example, allowing access from an entire network when an application only requires communication with a specific server can create additional attack paths. Narrower rules can reduce that exposure while still supporting legitimate business operations.
Security teams should periodically evaluate whether access can be restricted by source, destination, application, port, protocol, or other relevant conditions.
The goal is not to create complicated policies for the sake of complexity. Instead, the objective should be to create rules that are understandable, necessary, and appropriately limited.
Build a Consistent Change Management Process
Firewall changes are often driven by legitimate business needs. A new application may require network access, an employee may need access to a resource, or an infrastructure migration may require changes to existing policies.
However, making changes without a consistent process can introduce mistakes.
A good change management workflow should include the reason for the request, the requested access, the potential security impact, approval requirements, and an appropriate review process. Once the change has been implemented, teams should also be able to determine whether it produced the expected result.
Automation can make this process more efficient, particularly in environments where security teams handle a high volume of policy requests. Automated workflows can help reduce repetitive manual tasks while maintaining appropriate controls around approvals and implementation.
Monitor Rule Usage
A firewall rule may exist in a configuration without being actively used. Understanding actual rule usage can help security teams make better decisions about cleanup and optimization.
Usage information can reveal whether a rule is receiving traffic, whether the traffic matches its intended purpose, or whether the rule may be a candidate for review.
This is particularly valuable when dealing with large rule sets. Manually inspecting thousands of rules is time-consuming and can make it difficult for teams to identify the highest-priority issues.
Usage analysis can therefore support more informed decisions about which rules should remain, which should be modified, and which may no longer be necessary.
Maintain Visibility Across the Network
Modern organizations rarely operate a single firewall in a simple network. Many use multiple firewall vendors, cloud security controls, remote offices, data centers, and hybrid infrastructure.
This complexity can make it difficult to understand how policies work together.
Organizations need visibility into their security policies across the environments they manage. Centralized visibility can help teams identify inconsistencies, understand access relationships, and investigate potential risks without relying entirely on individual device configurations.
A comprehensive network security management approach can bring together policy information and provide security teams with a clearer picture of how network controls are operating across the organization.
Make Compliance Part of the Process
Firewall policies can also play an important role in meeting security and regulatory requirements. Organizations in regulated industries may need to demonstrate that network access is controlled, reviewed, documented, and appropriately restricted.
Instead of treating compliance as an activity that happens only before an audit, organizations can incorporate policy review and documentation into everyday security operations.
Maintaining organized records of changes, approvals, reviews, and policy decisions can make audits easier while also improving overall security visibility.
Use Technology to Support Security Teams
As firewall environments become larger and more complicated, manual processes become increasingly difficult to maintain. Security teams may spend significant amounts of time reviewing rules, investigating access, processing change requests, and preparing reports.
Technology can help reduce this administrative burden.
Modern firewall management solutions can provide capabilities for analyzing policies, identifying optimization opportunities, reviewing rule usage, automating changes, and improving visibility across complex environments. The right technology does not replace security expertise; instead, it gives security professionals better information and more efficient workflows.
The key is to choose an approach that fits the organization’s infrastructure, security requirements, and operational processes.
Building a More Effective Firewall Strategy
Strong firewall security is not achieved simply by adding more rules. In many cases, better results come from understanding existing policies, removing unnecessary complexity, and creating a repeatable process for managing change.
Organizations should regularly evaluate their rules, establish clear ownership, follow least-privilege principles, monitor usage, and maintain visibility across their network environment. Combining these practices with automation and centralized analysis can help security teams manage growing firewall environments more efficiently.
For organizations looking to improve visibility, analyze firewall policies, optimize rules, and automate policy changes, Opinnate provides network security policy management capabilities designed to support these needs. By bringing policy analysis, optimization, and automation into the security workflow, organizations can take a more structured approach to managing firewall policies while strengthening their overall network security posture.